How To Remove Ransomware in 2026: Step-by-Step Recovery Guide


Few types of malware are as dangerous as ransomware. It encrypts your files, making them unusable, or even locks you out of your entire operating system. Attackers then demand payment to restore access to your data.
This article explains why you should never pay the ransom and what to do instead if you're hit.


If you suspect ransomware, disconnect the infected device from the internet immediately to prevent the malware from spreading across your network.
Do not pay the ransom. There’s no guarantee you’ll get your data back, and paying the ransom both funds criminal activity and may make you a repeat target.
Don’t delete the encrypted files. Instead, back them up to an external drive in case you can recover them later.
First, remove the ransomware using Windows’ built-in virus and threat protection. Then, scan your system with a second anti-malware tool.
After that, try to recover your encrypted files using a decryption tool or a backup. If you’re unsure, get professional help.
What Is Ransomware?
Ransomware (also called “extortion malware” or “extortion software”) is one of the most dangerous types of malware. It targets individuals, businesses, and even government agencies.
Here’s what an attack might look like: you turn on your computer, and suddenly all your documents, photos, and files are encrypted and won’t open. In some cases, your PC may not even boot normally. Instead, you see a bold ransom demand: pay a set amount in Bitcoin within a few days to “unlock” your system.
No. Both the FBI and the Cybersecurity and Infrastructure Security Agency (CISA) strongly advise against paying. There is no guarantee you’ll receive a working decryption key, and paying the ransom funds further criminal activity.
For more details, take a look at the FBI’s page on ransomware.
Immediate Steps: What To Do after a Ransomware Attack
If you realize your device is infected with ransomware, every minute counts. Stay calm and follow these steps to save your data and remove the malware from your system.
Disconnect the device from the network and turn off Wi-Fi and Bluetooth. This stops the ransomware from spreading or communicating with the attackers’ servers.
Unplug the ethernet cable
Ransomware can spread to other devices on your network: your laptop, NAS (network-attached storage), home server, other computers, smartphones, and even smart TVs. The sooner you stop it, the better.
Unplug the affected device from the network right away. Remove the Ethernet cable and turn off Wi-Fi and Bluetooth. In Windows, you can disable Wi-Fi by going to “Start” → “Settings” → “Network & Internet”:

Turn off Wi-Fi in settings to prevent the ransomware from causing more damage.
You can disable Bluetooth in “Settings” under “Bluetooth & devices”:

Turn off Bluetooth in settings to stop the ransomware from infecting other devices.
Important: Keep the device offline until the ransomware is completely removed. Handle any steps that require an internet connection, like downloading tools, on a second, uninfected device.
Document the ransomware attack
Take screenshots of the ransom note. Write down the file extensions of the encrypted files (like .locky, .encrypted, or .wncry), the time of the attack, and which drives were affected. You’ll need this information to report the incident to authorities and to identify the ransomware.
Back up encrypted files
Do not delete the encrypted files. Instead, back them up to an external drive, such as a USB flash drive or external hard drive, and keep them safe. You may be able to recover them later using decryption software.
Be careful with cloud storage: services like OneDrive or Google Drive sync files automatically, which can overwrite your clean backups with encrypted versions. Disable cloud sync before that happens, and back up your files manually instead.
If ransomware has locked your system and you can’t access your files or USB drives, try booting your PC in safe mode. Windows runs only essential processes in this mode, which usually stops the ransomware from running and may let you reach your files through File Explorer.
You can read more about this in the section “How to Start Windows in Safe Mode”.
Report the attack
Ransomware is a crime. After securing your files, report the attack to your local police station or through the police online reporting portal or directly with the FBI.
Include all the evidence you’ve gathered: screenshots, the ransom note, the type of ransomware, affected file extensions and drives, and the time of the attack.
Remove Ransomware and Decrypt Your Data
If you want to remove the ransomware on your own and recover your files, you’ll need malware software and a clean second device.
Note: Removing ransomware and recovering encrypted files takes some technical know-how. If you’re unsure, the infection has spread across your network, or critical data is at risk, we recommend contacting an IT specialist.
Perform all downloads and research on a separate, uninfected device. Once you've downloaded the tools, transfer them to the infected machine using a USB drive.
Identify the ransomware
Removing ransomware alone won’t decrypt your files. For that, you need the right decryption software (called a “decryptor”).
Because ransomware comes in many variants, you first need to identify which one you’re dealing with so you can find the right decryptor. Once you’ve identified the ransomware variant, remove the malware before attempting file recovery. Here’s how:
Step 1: Using a USB drive, copy an encrypted sample file and the ransom note (as a text file) from the infected computer to your clean second device. Then upload these files to one of the following services:
ID Ransomware: Upload an encrypted file and the ransom note as a text file. The service compares them against a large database and tells you which ransomware variant you’re dealing with, often along with a matching decryptor.
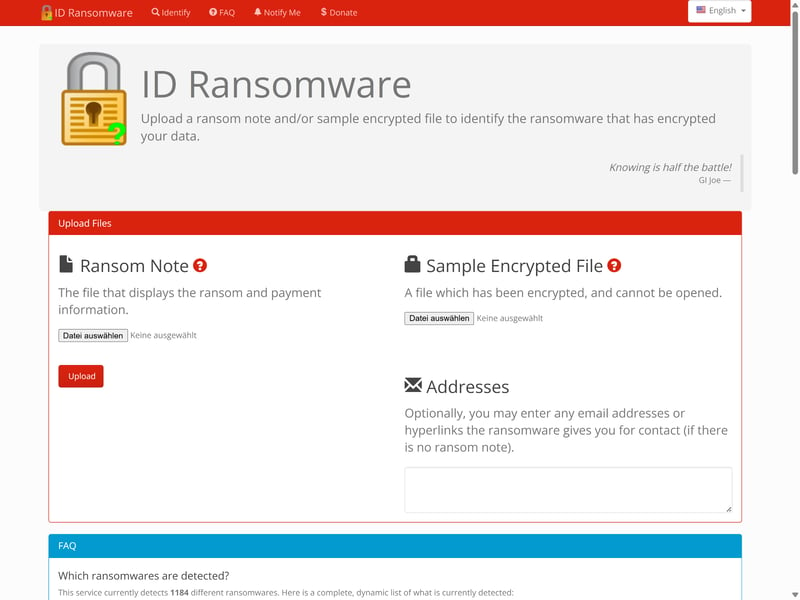
On ID Ransomware, you upload the ransom note or an encrypted file to identify the ransomware variant.
Nomoreransom.org: “No More Ransom” is a joint initiative by Europol, the Dutch National Police, and cybersecurity companies including Kaspersky and McAfee. The website features the “Crypto Sheriff,” a tool that helps you identify ransomware and find a matching decryptor.
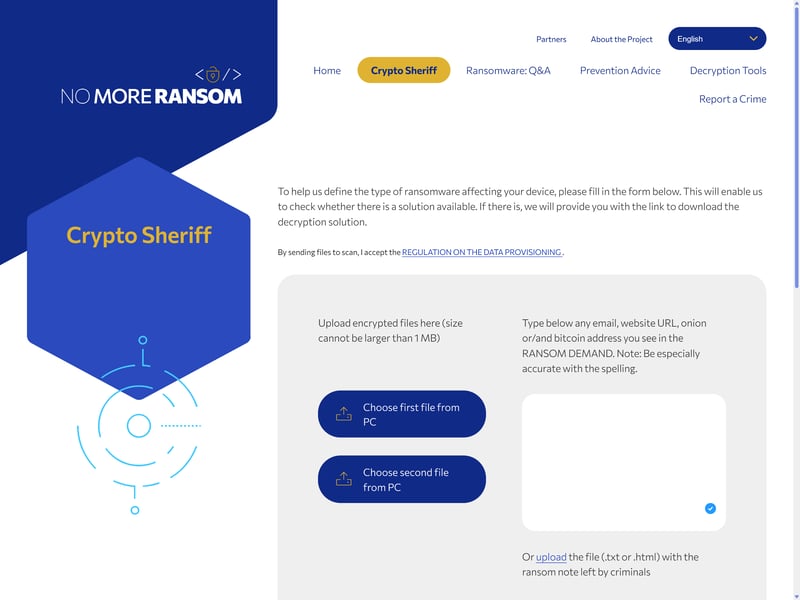
NoMoreRansom’s “Crypto Sheriff” helps you identify ransomware and suggests matching decryptors.
Step 2: Once you know the ransomware variant, look for the matching tool under “Decryption Tools.” NoMoreRansom currently offers more than 136 free decryption tools for various types of ransomware.
Step 3: Save the downloaded decryption software to a USB drive. Always remove the ransomware from your system before you try to decrypt your files. Otherwise, they’ll just get infected again.
Even if no matching decryption software exists right now, keep your encrypted files. New tools often appear weeks or months after a ransomware strain emerges.
Meanwhile, remove the ransomware from your system. Check sites like nomoreransom.org regularly for new decryption tools.
Remove ransomware
Once you've backed up your files and identified the ransomware strain, it’s time to clean your system.
Windows’ built-in virus and threat protection (Defender) includes a malware scanner, but we recommend using at least one additional tool. Windows Defender provides solid baseline protection and catches most known threats, but it can struggle with newer strains.
Specialized tools like Malwarebytes, Norton, or Bitdefender use additional detection methods and can catch threats a single scanner might miss.
Download an anti-malware program on a second, clean computer and save it to your USB drive.
Start Windows in safe mode
Next, boot the infected computer in Safe Mode. In this mode, Windows loads only essential functions, which usually keeps the ransomware inactive.
Booting into safe mode offers two major advantages: it stops ransomware from spreading, and it lets you access your files, even if the system is completely locked in normal mode.
Here’s how to do it:
Step 1: Click “Start” → “Power,” then hold down the Shift key while clicking “Restart.”
Alternatively, go to “Start” → “Settings” → “System” → “Recovery,” then under “Advanced startup,” click “Restart now.”

Use Windows 11’s system settings to perform an advanced startup and boot into Safe Mode.
Step 2: After restarting, you’ll see a screen titled “Choose an option.” Select “Troubleshoot” → “Advanced options” → “Startup Settings,” then restart your PC again.

In the options menu, select “Troubleshoot,” followed by “Advanced options” and “Startup Settings.”
Step 3: In the next menu, press the “5” key to start safe mode with networking.
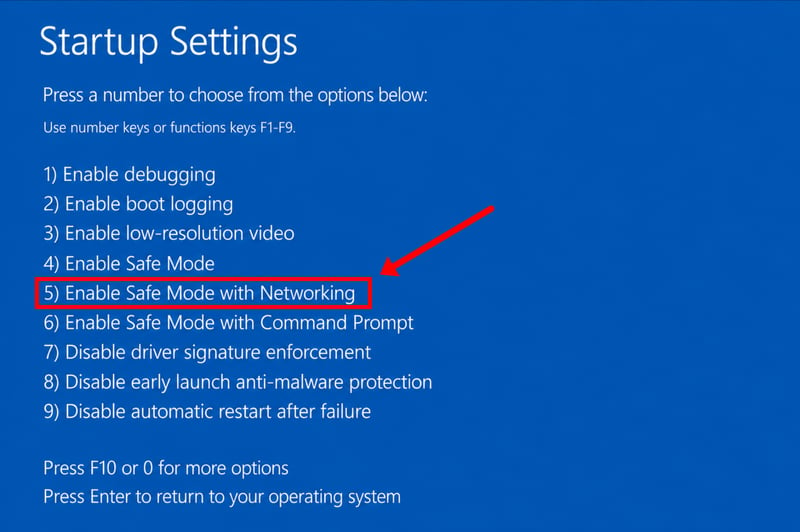
Boot Windows in safe mode to bypass the lock and manage your files.
What to do if safe mode doesn’t work
Some ransomware variants block access to Windows entirely. You’ll see only the ransom note and can’t use your system normally. If this happens, try forcing your way into safe mode:
Force your PC to shut down during startup three consecutive times. Windows will detect the problem and automatically show you the advanced startup options.
If that doesn’t work either, your last option is to skip safe mode entirely and boot from a USB drive with an emergency scanner instead.
You’ll need a flash drive with at least 2 GB of storage and a second, clean PC to create it.
- 1.
On a clean, uninfected computer, download a rescue tool as an .ISO file, such as ESET SysRescue Live or Kaspersky Rescue Disk.
- 2.
Download Rufus, a free tool for creating bootable USB drives.
- 3.
Open Rufus, select the .ISO file you downloaded, choose your USB drive as the target, and click “Start.” This takes a few minutes.
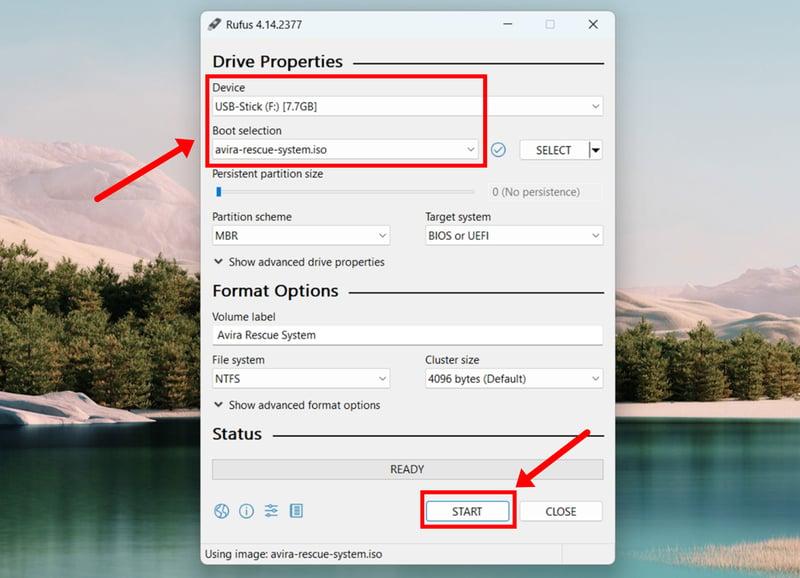
In Rufus, select the .ISO file and choose your flash drive. Then click Start to create the boot drive.
- 4.
Plug the USB flash drive into the infected device and restart it. To boot from the drive, press a specific key during startup. The key varies by manufacturer, but F11 or F12 are the most common.
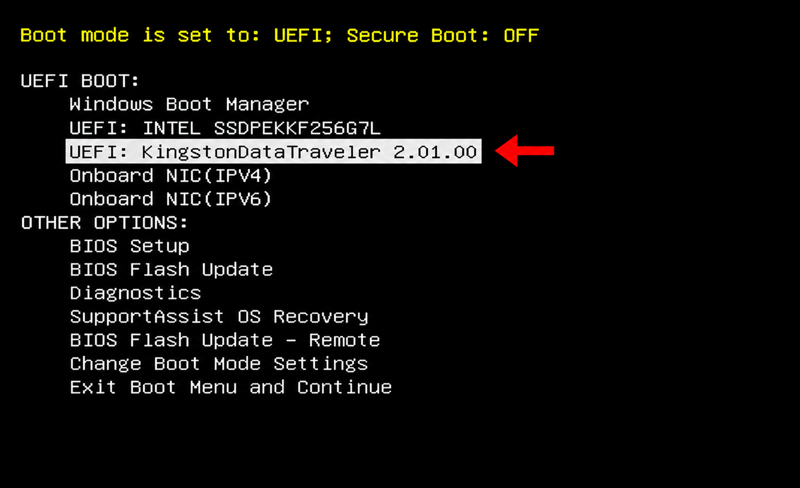
In the boot menu, select the USB drive to launch the anti-malware program.
- 5.
Run a system scan with the tool and remove any malware it finds.
Run a malware scan
Once your computer is in safe mode, run a full system scan. Our first choice for this is the built-in Windows virus and threat protection. On Windows 11, you’ll find it under “Settings” → “Privacy & Security” → “Windows Security.”
Under “Scan options,” select the full system scan instead of the quick scan.
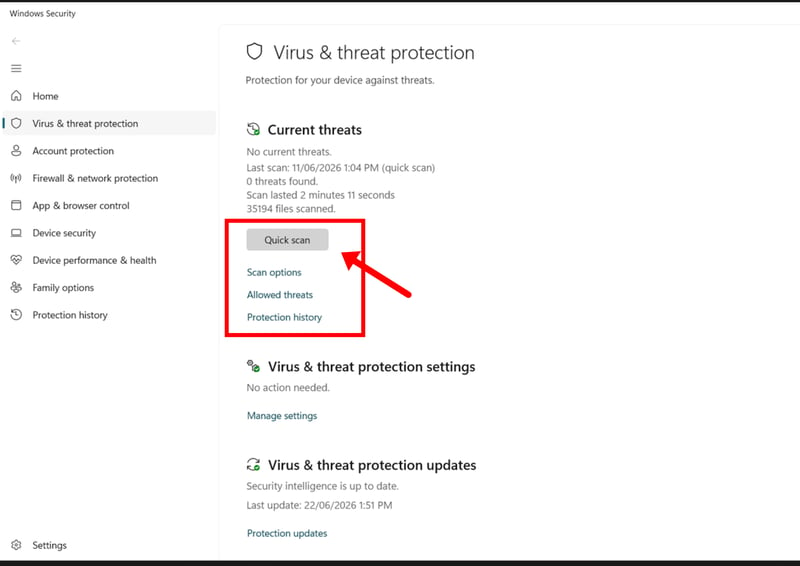
We ran the first malware scan using Windows’ built-in virus and threat protection.
Since no single scanner catches every threat, run a second scan using the malware scanner stored on your USB drive.
If either tool finds malware, it will move the files to quarantine or remove detected threats.
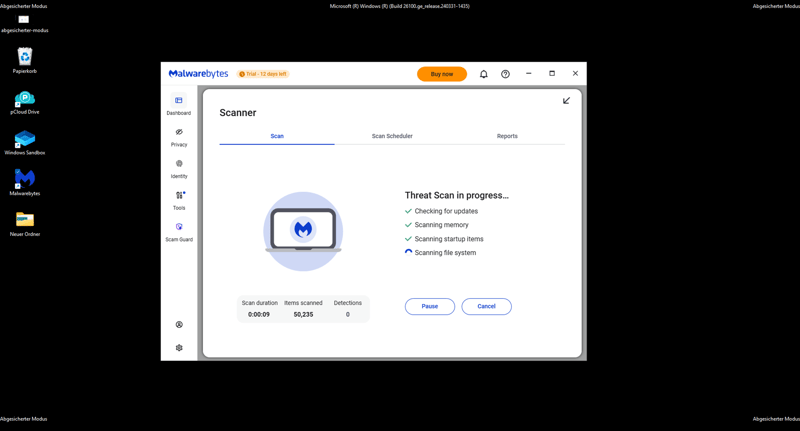
Run a system scan in Safe Mode using an anti-malware tool. Here’s an example using Malwarebytes.
Restart your PC normally and check whether the system is functioning normally. If you don’t see a ransom demand, you’ve most likely removed the ransomware successfully.
If the problem persists, you’ll need to reinstall Windows completely. Format all drives and set up the system from scratch.
Recover encrypted files
Once your system is malware-free, copy your backed-up encrypted files back to the cleaned system and try to decrypt them. Use the decryption tool in the section “Identify Ransomware.”
Not all decryptors work the same way, so the exact steps vary. Some tools decrypt files automatically, while others require an unencrypted sample file. Read the instructions for your specific tool carefully before you start.
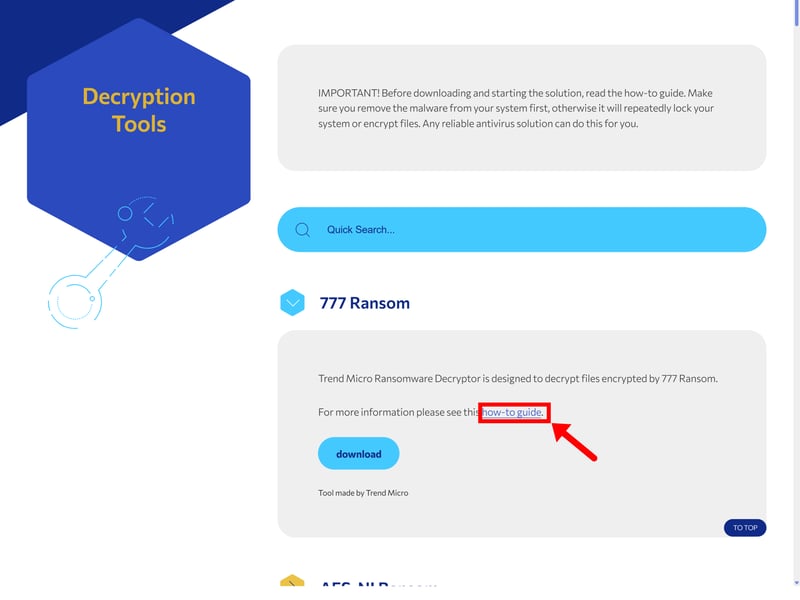
NoMoreRansom provides instructions (in English) as a PDF for every decryption tool.
How To Remove Ransomware From Your Smartphone
Smartphones aren’t safe from ransomware either. Android devices are especially popular targets for cybercriminals because Android allows app installation from multiple sources.
Ransomware usually gets onto your phone in one of two ways:
Fake apps: Cybercriminals disguise ransomware as legitimate apps. Installing one infects your device.
Drive-by downloads: Hacked or malicious websites can silently install ransomware by exploiting security flaws or tricking you into downloading infected files.
Here’s how to remove ransomware from your smartphone:
Step: Revoke app permissions
Go to Settings → Apps, tap each app, and check its permissions. Revoke permissions from any suspicious app, especially device admin or accessibility access. Otherwise, the app might block you from uninstalling it.

In the app info, you can see which permissions an app has and change them.
Step: Boot into safe mode
Boot your smartphone in Safe Mode. In this mode, only pre-installed system apps load, which keeps the ransomware inactive and makes it easier to remove. On most devices, press and hold the power button, then long-press “Power off.”
Alternatively, turn off your device. As you turn it back on, hold the volume-down button as soon as the “Powered by Android” logo appears.

Boot your smartphone in Safe Mode.
Step: Uninstall Suspicious Apps
In Safe Mode, go to “Settings” → “Apps.” Look for recently installed or unfamiliar apps and uninstall them. Be especially wary of apps you don’t remember installing or those that request unusual permissions.
Step: Run a Malware Scan
Use Google Play Protect or a security app like Malwarebytes to scan your device and remove any remaining threats.
Step: Factory Reset as a Last Resort
If the ransomware won’t go away, your last option is a factory reset. This wipes all data from your device, so back up any important files to the cloud or a computer if they aren’t already encrypted.
How To Prevent Ransomware
As with any online threat, your best defense against ransomware is prevention. These steps will significantly lower your risk of an attack:
Final Thoughts: How To Handle Ransomware
A ransomware attack is serious, but not hopeless. The rule of thumb: don’t pay the ransom. With the right steps, and possibly professional help, you can often remove the malware. Depending on the ransomware strain, decryption tools may also be available to recover your files, although many newer ransomware variants currently have no publicly available decryptor.
Your best protection, though, is prevention. Regular backups on an external drive and careful handling of suspicious emails, apps, and websites will greatly reduce your risk of a successful ransomware attack.
FAQ
Ransomware is a type of malware that encrypts your files and makes them inaccessible. Attackers then demand a ransom, usually in cryptocurrency, in exchange for the decryption key.
No. Authorities and cybersecurity experts strongly advise against it. There’s no assurance you’ll get your files back, paying encourages further criminal activity, and it makes you a repeat target.
No. Antivirus software can remove the ransomware itself, but it cannot decrypt files that have already been encrypted. For that, you’ll need specialized decryption tools designed for the specific ransomware strain. Free tools are available at nomoreransom.org.
The most important step is regularly backing up your data to an external drive. That way, your files stay safe even if you’re attacked. Always keep your operating system and software updated, since many attacks exploit known security flaws. And be cautious with email attachments and links, because phishing is the most common way ransomware spreads.