Two-Factor Authentication: How to Protect Your Accounts


Passwords can be cracked, guessed, or stolen. And when that happens, a single login is often all it takes to access emails, accounts, or sensitive business data. Two-factor authentication (2FA) protects against exactly that.
2FA adds a second layer of security on top of your regular password. That could be a code sent to your phone or a confirmation through an app. Even if your password falls into the wrong hands, your account stays protected. Here's how 2FA works and what methods are available.


What Is Two-Factor Authentication?
The idea behind two-factor authentication (2FA) is right there in the name: it adds a second factor to your security. With 2FA enabled, logging into an online service requires not just something you know (for example, a strong password) but also something you have (for example, a signature or a smartphone).
So even if your password ends up in the wrong hands, this double verification keeps your online identity safe from unauthorized access.
The terms "authentication" and "verification" are often used interchangeably, even though they describe different parts of the same process. Users verify their identity by providing login credentials, and then the system authenticates them. Verification is from the user's perspective, authentication is from the system's. But the end result is the same.
How Does Two-Factor Authentication Work?
With 2FA enabled, you enter your username and password as usual. Then you need to confirm your identity in a second step, proving that it's really you logging in. There are several ways to do this:
One-time codes via SMS
You receive a code (usually six digits) via text message on your phone and enter it during login.
This method is easy to use but vulnerable to attacks like SIM swapping or SMS interception.Authenticator apps
Dedicated apps like Google Authenticator, Microsoft Authenticator, or Authy generate time-limited verification codes automatically after setup.
This method is significantly more secure than SMS because the codes aren't transmitted over a cellular network.

Authenticator apps like Microsoft Authenticator generate new one-time passwords every 30 seconds for your services.
Push notifications
With this method, you get a notification on your smartphone from your email provider's or bank's app, and you simply tap to approve the login.
This approach is convenient and secure, especially when your phone is also protected by biometric locks. However, phishing attacks can sometimes trick users into approving fraudulent requests ("push bombing").Biometric verification
You can also verify your identity using a fingerprint, facial recognition, or iris scan.
Biometric confirmation is hard to fake, but it's not perfect. For example, there are ways to fool facial recognition systems.Hardware tokens
You can also use dedicated devices like a YubiKey or TAN generators that create one-time codes. They work like authenticator apps, but as physical security devices you purchase separately.
From a security standpoint, hardware tokens are still the gold standard. The key has to be physically present, which makes phishing or remote attacks nearly impossible. The downside is that you always need to have the token with you and within reach.
Each method has its own trade-offs between security and convenience. SMS-based 2FA, in particular, is now considered relatively insecure. If multiple methods are available, go with a safer alternative.
Should You Use 2FA?
Short answer: Absolutely. Two-factor authentication offers simple but powerful protection against unauthorized access. For sensitive services like email, cloud storage, or banking, 2FA should be standard by now. Government agencies like CISA strongly recommend it.
The benefits of 2FA are clear:
Stronger security
With 2FA enabled, your password alone is useless to hackers and data thieves. They'd also need your smartphone or hardware token.Protection against password leaks
Even if your credentials end up exposed in a data breach, attackers can't log in without the second factor.Multiple methods to choose from
There are plenty of 2FA options and many free apps for popular smartphones and tablets. Pick the method that fits your setup best.Better visibility into login activity
Many 2FA methods actively notify you about new login attempts. This can help you spot potential attacks early.Extra security for teams
For businesses with shared logins or cloud access, 2FA is an important safeguard against both internal and external threats.
That said, the extra security comes with some drawbacks:
Dependent on your devices
There's no guarantee your authentication device will always be available. If your phone is stolen, damaged, or simply out of battery, you might be locked out of your own accounts.A false sense of security
If you lose your second factor, you're in the same position as an attacker. Also, recovery options like backup codes or email recovery can themselves become targets. 2FA is not a free pass: you still need to stay vigilant.A bit inconvenient day-to-day
The extra step can be annoying, especially if you log in frequently or switch between devices a lot.
Despite these limitations, the benefits of 2FA clearly outweigh the downsides.
Tip: If you don't want to verify via 2FA every single time you log in, you should at least enable it for new devices or unrecognized browsers. That way, if your password ever falls into the wrong hands, no one can access your account without you knowing.
How Do You Set Up 2FA?
Setting up two-factor authentication looks a bit different depending on the service and method. Some platforms let you choose from several 2FA options, while others only support one specific method.
You'll usually find the option in your account settings under something like "Security," "Login Protection," or "Verification." From there, the service will walk you through the activation process step by step.
Example: 2FA With 1Password
As mentioned, the setup process varies from service to service. Here's how it works with the password manager 1Password:
Step 1: Log in to the web dashboard. Go to "My Profile," click "More Actions," and select "Manage Two-Factor Authentication."
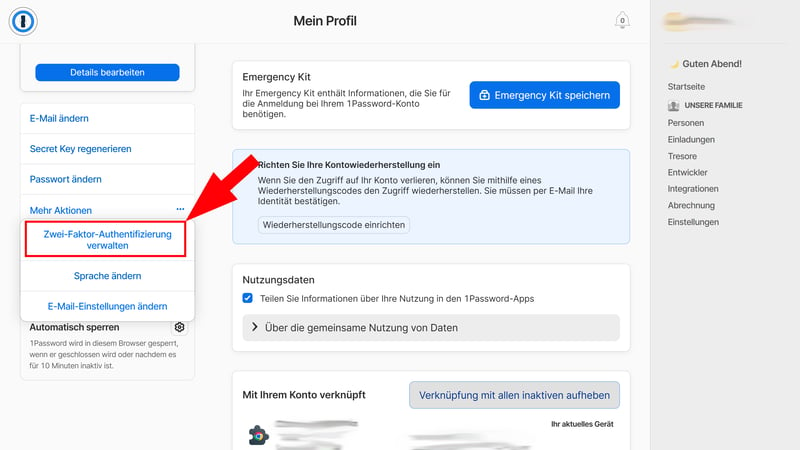
Open the 2FA settings.
Step 2: You'll see two options: authentication via an authenticator app of your choice, or via a physical device. We're going with the first option.
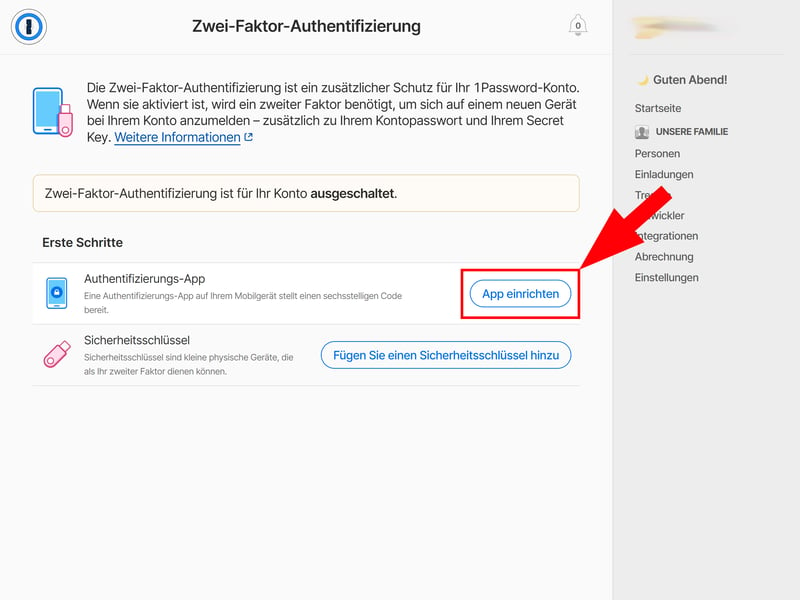
Set up a new 2FA method.
Step 3: A QR code will appear on screen.
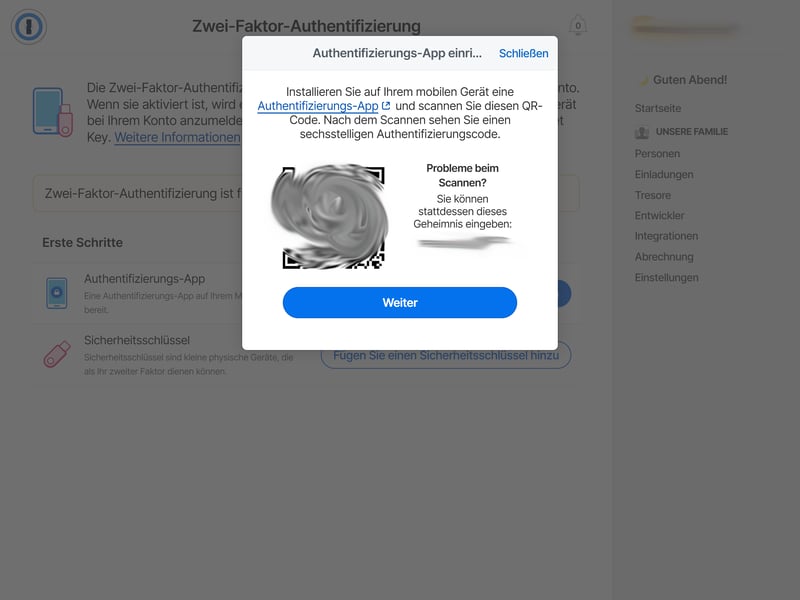
Linking is done easily via QR code.
Step 4: Scan the QR code with the authenticator app of your choice. In this example, we're using Microsoft Authenticator. You'll find the scan button in the bottom left corner:

Open your authenticator app and scan the QR code.
Step 5: 1Password has now been added to your Microsoft Authenticator account. All you need to do is enter the one-time code shown in the authenticator app into the input field on 1Password.
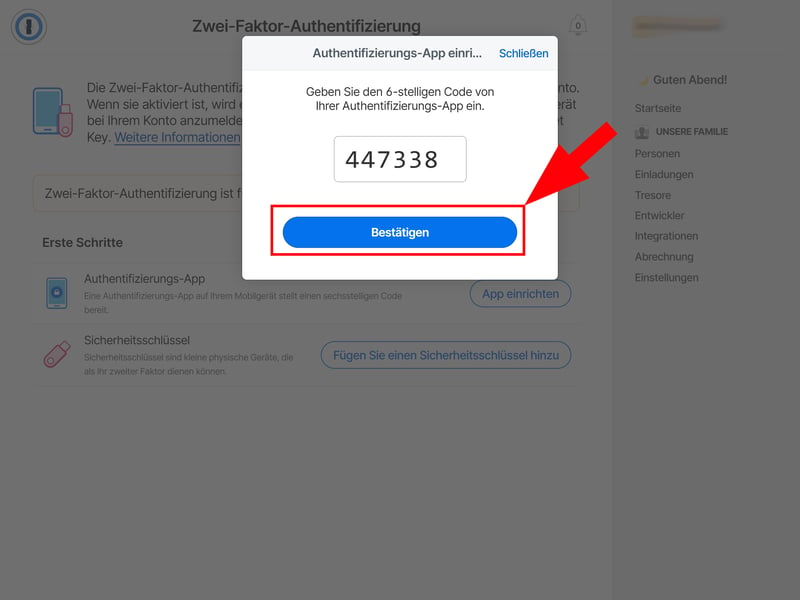
Enter the one-time code and click "Confirm."
Step 6: Your account is now linked. From now on, every time you log in from a new device, you'll need to confirm it with your authenticator app.
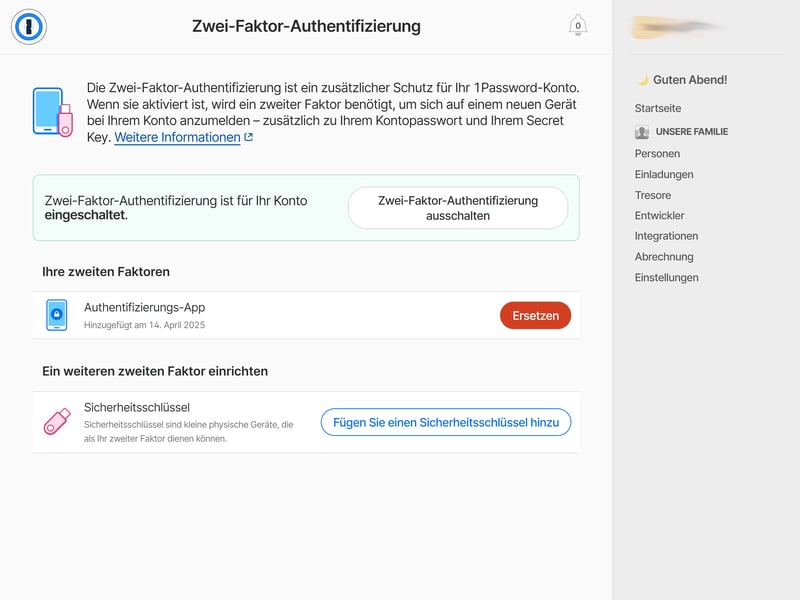
2FA has been set up successfully.
Conclusion
A strong password alone isn't enough. Login credentials get stolen all the time through phishing attacks and data breaches. Two-factor authentication (2FA) adds an extra layer of security to your accounts that attackers typically can't get past, or at least not without significant effort.
Whether it's SMS, an authenticator app, or a hardware token: most software solutions now support at least one 2FA method. You should definitely enable it for sensitive areas like email, cloud storage, or online banking. If not for every login, then at least for sign-ins from new devices. The added security is well worth the small extra step.
Frequently Asked Questions
Two-factor authentication (2FA) is a security method that requires a second form of verification after entering your password. This could be a code sent to your phone, a confirmation through an app, or a physical security key. It makes it much harder for attackers to access your account, even if they somehow get hold of your password. In short, 2FA adds an extra layer of protection against unauthorized access.
Yes. A strong password protects you from brute-force attacks, but it won't necessarily keep you safe from phishing, data breaches, or malware. 2FA acts as a safety net in case your password falls into the wrong hands.
Usually, yes. Most services offer authenticator app or SMS-based 2FA at no extra cost. If you want the highest level of security (e.g., with a hardware token), there may be a one-time purchase cost for the device.
If you lose the device you use for your second factor, you should register a new one as quickly as possible. Many services offer backup codes or recovery options to help you regain access. Make sure to store these in a safe place, separate from your phone.
SMS-based 2FA is better than no 2FA at all, but it's less secure than other methods. It's vulnerable to SIM-swapping attacks and SMS interception. Whenever possible, use an app-based method or a physical security device instead.
Not necessarily. Many services let you mark familiar devices or browsers as "trusted." Once you do, you'll only need to complete the 2FA step when signing in from a new device or location.